

Third party risk management

Continuously refreshed TPRM scores across security, financial, legal, compliance and ESG — surfaced directly in your workflow, and validated regularly by the Vertice team.
Layer your internal assessments and ratings from tools like Vanta, OneTrust, and Dun & Bradstreet on top of Vertice insights.

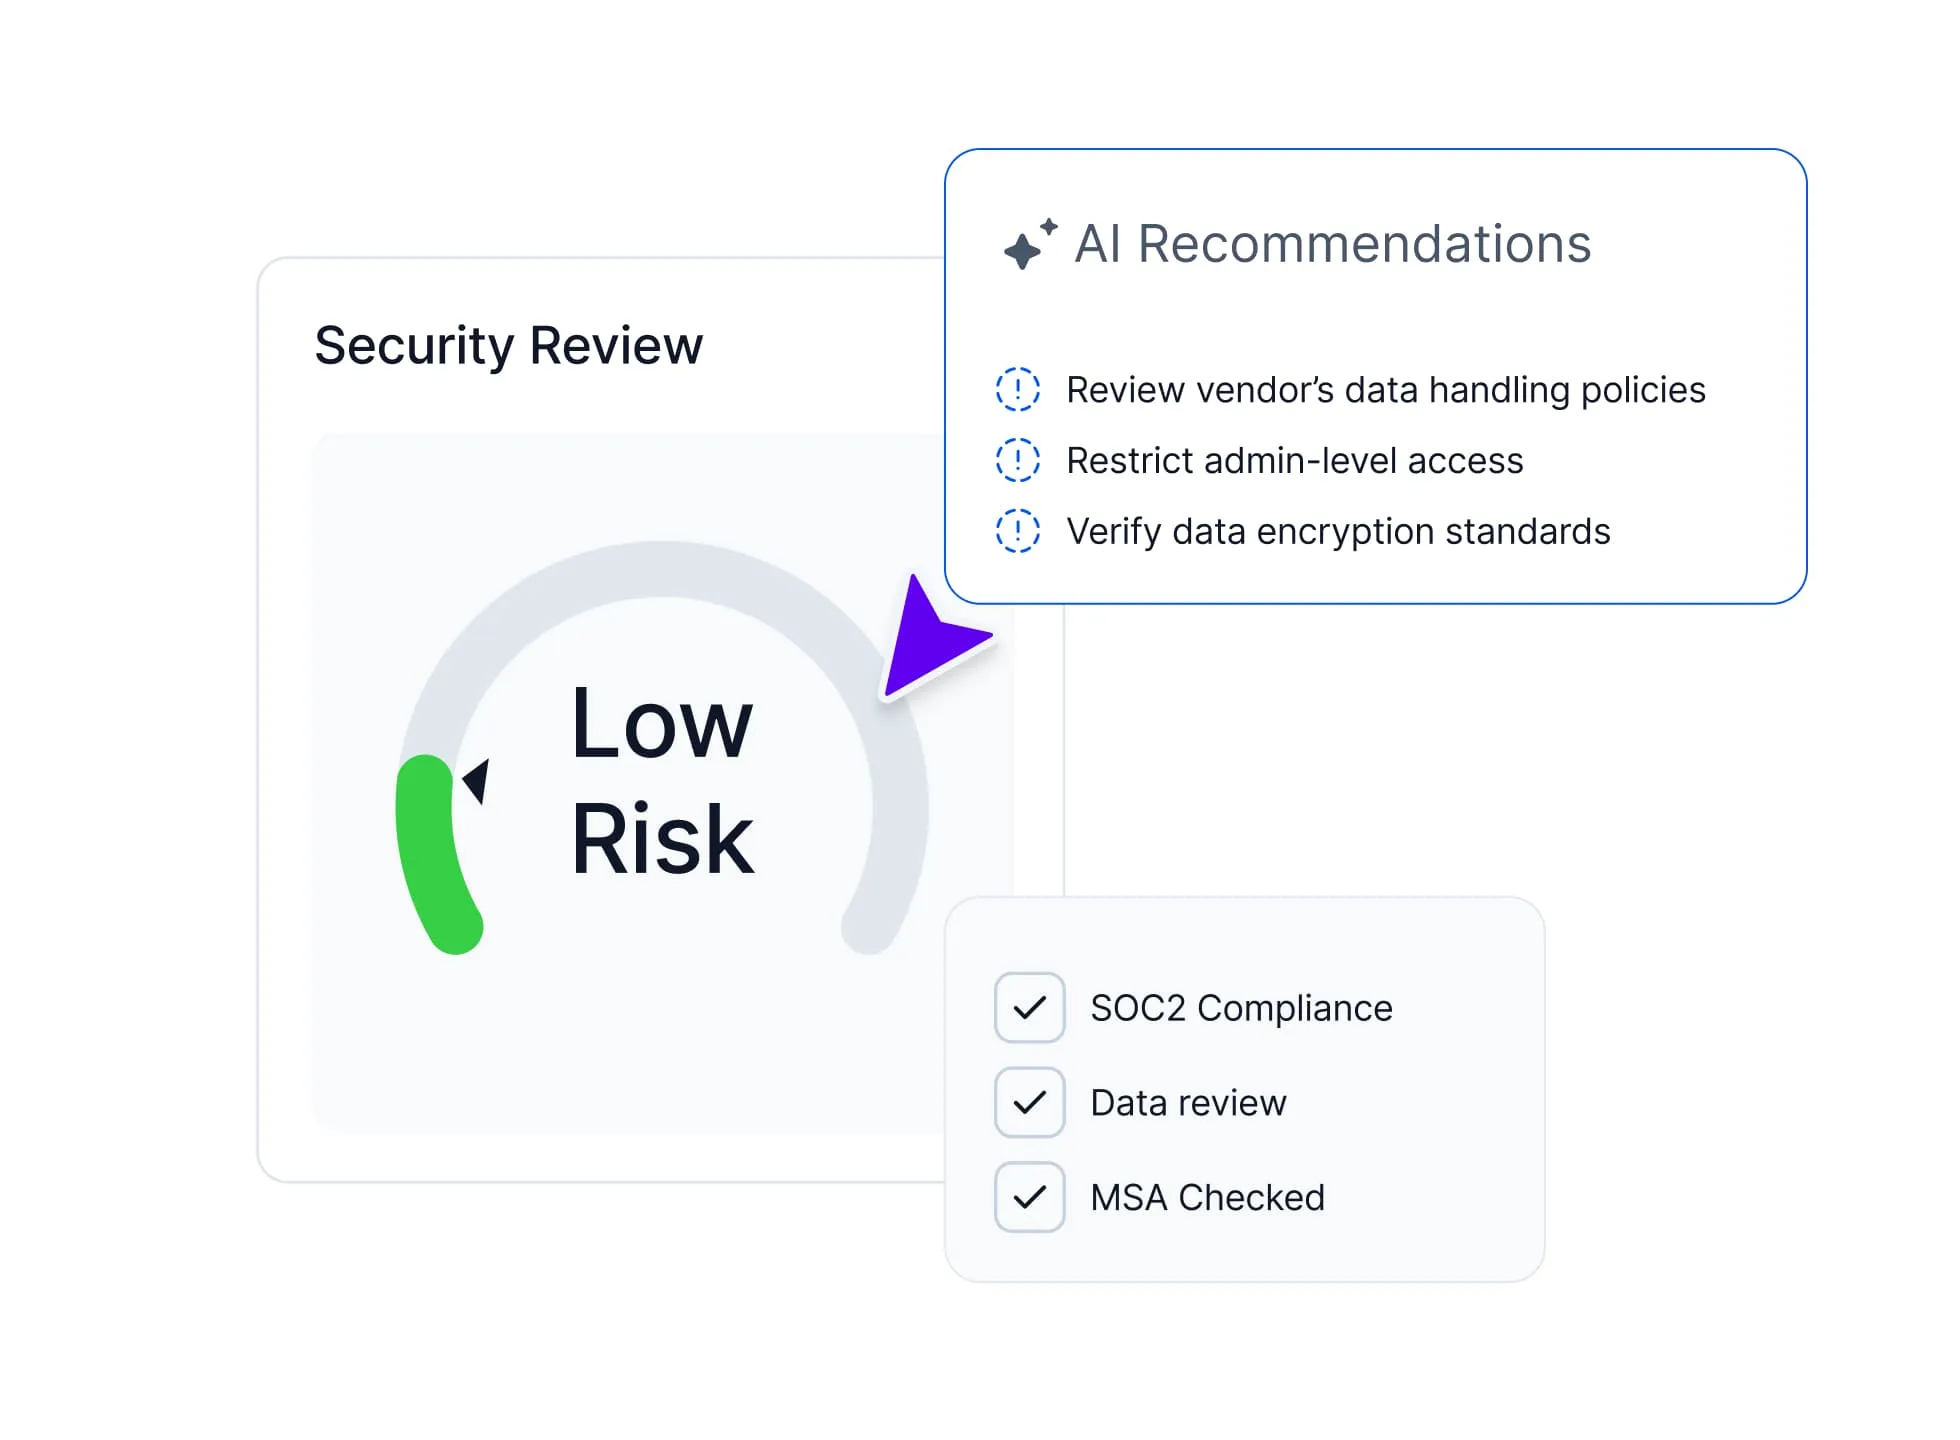
Embed AI agents directly into your workflows to automatically review vendor risks against your legal, compliance, and internal policies.


The need-to-knows about Vertice
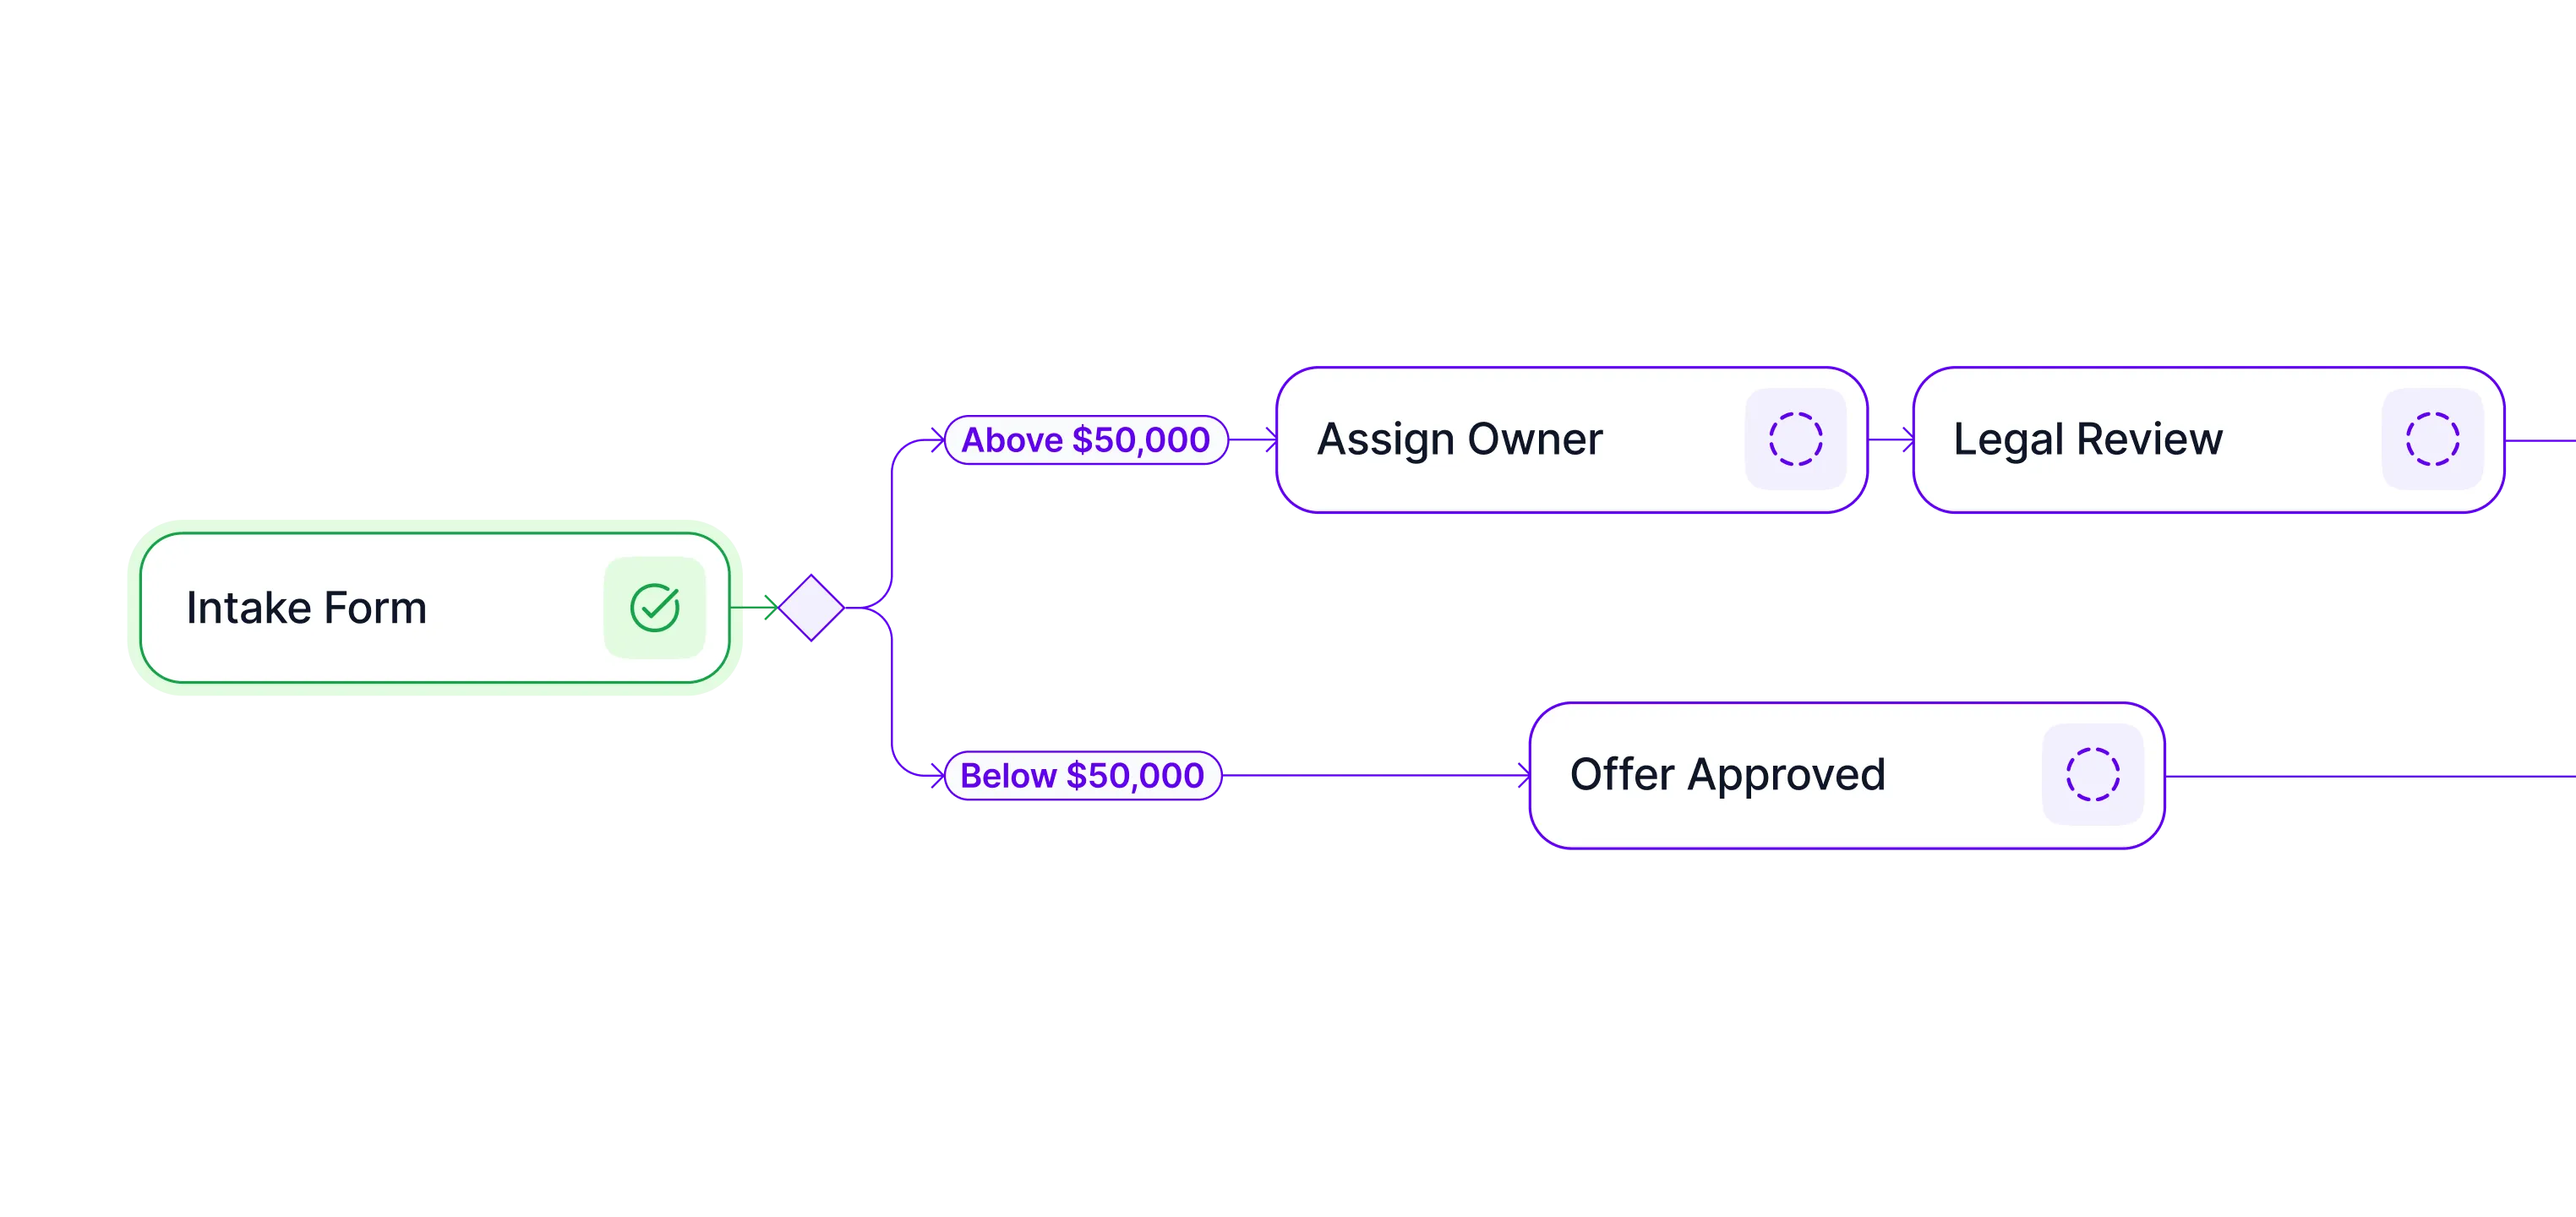
Vertice embeds security, legal and compliance checks directly into Intake-to-Procure, with AI agents reviewing vendor risk within each workflow. Teams gain rapid access to summarized contract terms, ISO certifications and compliance information for vendors, allowing legal, security and finance teams to quickly assess risks before approving purchases or renewals.
Each supplier has a continuously refreshed risk score across security, financial, legal, compliance and ESG factors, built from public sources and proprietary research. Teams can layer in their own ratings from tools like Vanta, OneTrust and Dun & Bradstreet, see the likely impact on the business and decide whether a review, a mitigation step or an extra approval is needed before the purchase goes ahead.
Vertice enables organizations to send standard or custom security questionnaires to vendors, collect assessment reports, and attach them directly to contracts. Our workflows also include a security review subprocess, guiding vendors through risk scoring and approval to ensure compliance and operational safety.
Responses, certificates and reports stay on the supplier record, so evidence collection for an audit happens in one place instead of across inboxes and spreadsheets.
Vertice’s AI workflows embed compliance and legal checks directly into procurement processes. Every contract or renewal follows structured steps, triggering approvals from legal, compliance, and IT stakeholders, ensuring consistent risk management across the SaaS supplier lifecycle.
Supplier Risk Management involves identifying, assessing, and mitigating risks related to third-party providers from software vendors to hardware and services providers. It includes monitoring compliance, security certifications, and contractual obligations to ensure vendors meet organizational standards and minimize exposure to operational, financial or regulatory risks.
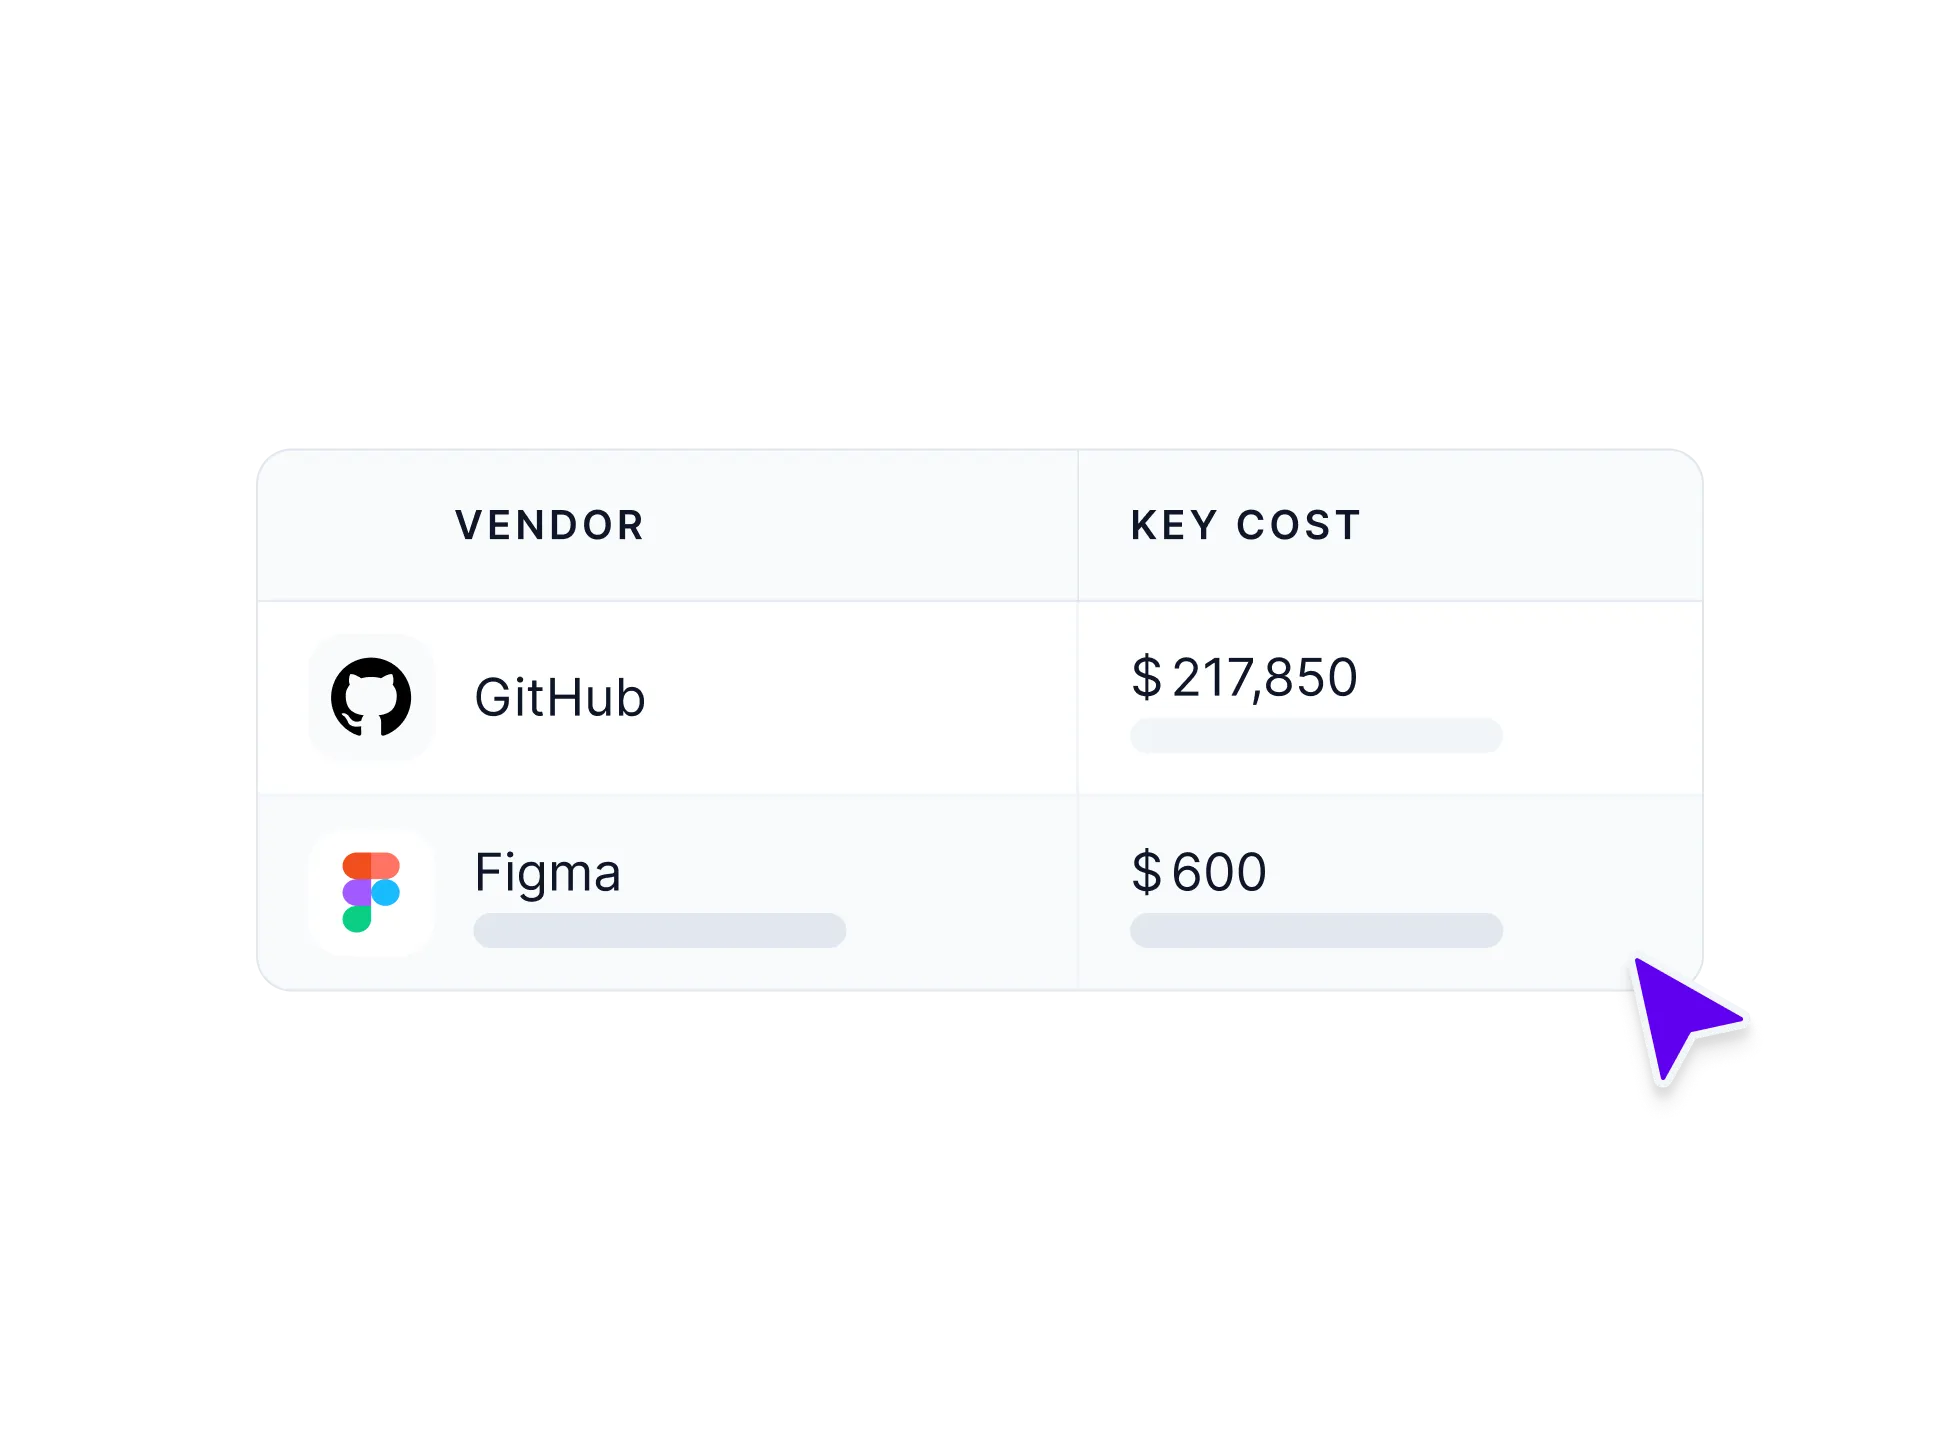
Vertice goes beyond point-in-time reviews by giving teams ongoing supplier risk management solutions that help them continuously manage supplier risk across their supplier portfolio. It centralizes key supplier data, tracks supplier performance, and surfaces areas of increased risk exposure as vendor contracts evolve.
With native third-party risk management embedded directly into the buying process, Vertice provides continuous monitoring and in-line security, legal and compliance checks. AI-driven risk scoring further helps teams make informed decisions at every stage, ensuring that procurement choices are backed by actionable insights.
As a practical vendor risk management solution, Vertice strengthens oversight of third-party software providers within your wider supply chain, helping teams address potential data security risks, maintain regulatory compliance, and build more resilient vendor relationships. By embedding structured review and monitoring into procurement workflows, Vertice helps organisations proactively reduce supplier risk over time.
Vertice's supplier risk management software provides continuous monitoring of vendor risk by aggregating data from public sources, proprietary research and digital asset monitoring. Risk scores are refreshed automatically with regular human validation, so compliance tracking stays current between formal vendor reviews. When a vendor's risk profile changes – through a security incident, compliance gap or certification lapse – Vertice surfaces alerts directly within procurement workflows before the next contract or renewal step is taken.
Because scores cover cyber, financial, legal, compliance and ESG risk, a change in any of these areas can prompt a review. Teams can then agree remediation with the supplier early and limit the impact on the business, with real-time visibility of which suppliers need attention.
Risk checks start before a new supplier is approved. When a request enters Vertice, the workflow collects security questionnaires, certifications and contract terms, then routes the supplier to legal, security and finance for review. Suppliers only move to contract once the right compliance checks are complete, so risk is managed from the first step of supplier onboarding rather than after signature.
Vertice combines its own TPRM scores, built from public sources, proprietary research and continuous monitoring of digital assets, with ratings from tools teams already use, such as Vanta, OneTrust and Dun & Bradstreet. Bringing this risk data together gives teams one set of risk indicators for each supplier, covering security and cyber, financial, legal, compliance and ESGrisk.
For SaaS and technology suppliers, disruption usually comes from a security breach, a supplier in financial difficulty or a lapse in compliance. Continuous monitoring flags these changes early, so teams can review their risk exposure, agree mitigation steps or line up an alternative supplier before a renewal or outage leads to supply chain disruptions.